

Key TakeawaysBitget detected unauthorized outflows from its hot and warm wallets at 18:31 UTC on Thursday, September 24, 2026 and later put the loss at about $387.5 million across seven networks, inclKey TakeawaysBitget detected unauthorized outflows from its hot and warm wallets at 18:31 UTC on Thursday, September 24, 2026 and later put the loss at about $387.5 million across seven networks, incl
Bitget Hack Explained: How $387 Million Was Stolen Without a Single Key, and the THORChain Standoff Splitting Crypto

Key Takeaways
Bitget detected unauthorized outflows from its hot and warm wallets at 18:31 UTC on Thursday, September 24, 2026 and later put the loss at about $387.5 million across seven networks, including Ethereum and other EVM chains, the XRP Ledger, Zcash and TRON. It is one of the largest exchange thefts on record, behind Bybit's $1.46 billion in 2025.
No private keys were stolen and cold storage was untouched. According to CEO Gracy Chen, attackers exploited a flaw in a third party security product and stolen internal credentials to compromise a backend system in the wallet stack, forge transaction data, and trick Bitget's own approval flow into signing transfers that looked routine.
Bitget says user balances are unaffected and its User Protection Fund of more than $464 million will absorb the loss. Withdrawals are restarting in phases: Bitcoin on September 28, Ethereum on September 29, USDT on September 30, and remaining tokens, fiat and P2P by October 2. Trading and deposits never stopped.
The aftermath produced a public standoff. Chen formally asked THORChain to refuse service to the publicly listed attacker addresses as loot was swapped through the protocol into Bitcoin; THORChain declined, citing its permissionless design, while SlowMist and OKX founder Star Xu noted it had paused itself quickly when its own funds were at risk.
Bitget suspects North Korean linked groups based on IP patterns and onchain behavior, with Mandiant and SlowMist investigating, Circle and Tether freezing about $318,000 in stablecoins, and 5% bounties on offer for freezing or recovering assets.
What Happened on September 24
The breach surfaced the way exchange hacks usually do now: onchain analysts saw it before the announcement. Bubblemaps, Wu Blockchain and others flagged unusual outflows from Bitget addresses within the hour, users began posting about failed withdrawals, and Bitget's own systems logged the unauthorized transfers at 18:31 UTC. CEO Gracy Chen posted a security notice at 21:30 UTC and withdrawals were paused. The initial estimate of about $351.6 million covered roughly $183 million leaving EVM chains and a single striking move on the XRP Ledger, where two Bitget wallets sent 93.7 million XRP, worth about $143 million, to a fresh address. Two days later the exchange raised the total to $387.5 million after tracing additional affected transactions on Zcash and TRON, stressing that the revision reflected a fuller accounting of the original attack rather than a second breach. The stolen assets included XRP, ETH, USDT, USDC, USDT0, ZEC, XAUt, BNB, AVAX and TRX.
How It Was Done Without Stealing a Key
The most unsettling detail is that Bitget's keys were never taken. According to Chen's account, the attackers exploited a vulnerability in a third party security product and used stolen internal access credentials to compromise a backend system within the wallet infrastructure. From there they forged transaction data so that transfers to their own addresses appeared as ordinary, legitimate withdrawals, and Bitget's approval flow signed them. Cold wallets were not involved, and the exchange says the vulnerability has since been identified and fixed so that no further unauthorized transfers are possible. Mandiant and SlowMist are assisting the forensic work, and a full incident report is still pending.
The technique matters because it echoes the Bybit heist of February 2025, in which attackers manipulated what signers saw rather than breaking cryptography, and because Bitget says IP patterns and onchain behavior resemble prior operations linked to North Korean groups, though formal attribution rests with investigators. Together the two incidents suggest the frontier of exchange security has moved from key management to the integrity of the systems that present transactions for approval.
The Protection Fund Faces Its Biggest Test
Bitget's response leaned on a promise it made years ago. The exchange says its User Protection Fund, which holds more than $464 million and is separate from its proof of reserves system, will cover the full loss, meaning customers should not bear any of it. Trading and deposits continued throughout, and Bitget framed the withdrawal freeze as a security measure rather than a liquidity problem. The proof is in the restart: Bitcoin withdrawals resumed at 08:00 UTC on September 28, Ethereum and other EVM networks follow on September 29, USDT on September 30, and the remaining tokens, fiat channels and P2P services are due back by October 2, each phase gated on validation checks. Bitget has also announced separate 5% bounties for anyone who helps freeze or recover stolen assets, Circle and Tether froze about $318,000 in stablecoins, and Binance founder Changpeng Zhao publicly voiced support. The phased reopening is the exchange's first operational test since the attack, and the market will read any hiccup harshly.
The THORChain Standoff
Within a day, part of the haul was moving. On September 25, MistTrack, the tracing unit of SlowMist, reported that Bitget linked funds were entering THORChain for swaps and cross-chain transfers, and pointedly asked what responsibility a protocol carries once the source of funds is known, noting that nearly $1.2 billion of the $1.46 billion Bybit loot had moved through the same rails in 2025. On Saturday Chen escalated, posting that Bitget's attacker addresses were public and tracked and formally asking THORChain to refuse them service. "Decentralization is a design principle, not a shield for facilitating known stolen funds," she wrote. "The industry is watching."
THORChain expressed regret but declined, arguing it is permissionless in the same sense as Bitcoin, Ethereum or BNB Chain and has no address level blocking in its validator design. SlowMist and OKX founder Star Xu disputed that framing, observing that THORChain had paused its network quickly when its own funds were at risk. The swaps continued: CoinDesk identified 27 transactions moving about 2,390 ETH into 75.2 BTC, roughly $6 million, and tracing shows the attacker also routing through Uniswap, 1inch, Stargate, Across, Relay, Chainflip and Circle's cross-chain transfer protocol, with about $83 million in stolen XRP already on the move.
The dispute is the same argument crypto has been having all month from different angles. Cronos validators rolled back nearly two hours of history to reverse a $120 million exploit, Blockstream paused the Liquid Network and negotiated with its hackers on chain, and now a decentralized protocol has refused to intervene at all. Each choice is defensible on its own terms, and each carries a cost: chains that can intervene weaken finality, and chains that cannot become the preferred laundromat for the industry's worst actors.
What It Means for Traders on MEXC
The market reaction was contained, with Bitcoin and XRP absorbing the news and ETF inflows continuing, but the incident is a reminder that counterparty risk on any centralized venue is real and that the details of protection funds, proof of reserves and withdrawal policies deserve reading before a crisis rather than during one. Practical habits apply everywhere: keep long term holdings in self custody or spread across venues, keep exchange balances sized to active trading, harden accounts with two factor authentication and withdrawal safeguards, and be alert to the wave of phishing that follows every major hack, as impersonators pose as support teams offering help. Traders can follow the assets at the center of the story on XRP/USDT and ETH/USDT.
Disclaimer: This content is for educational and reference purposes only and does not constitute any investment advice. Digital asset investments carry high risk. Please evaluate carefully and assume full responsibility for your own decisions.
市场机遇
4实时价格 (4)
$0.020701
$0.020701$0.020701
USD
4 (4) 实时价格图表
本页面分享的文章均源自公开平台,仅供参考。该内容不代表 MEXC 的立场或观点。所有版权归 OoJae 所有。如果您认为任何内容侵犯了第三方的权益,请联系 service@support.mexc.com 以便及时删除。 MEXC 不保证任何内容的准确性、完整性或及时性,且不对基于所提供信息而采取的任何行动负责。本内容不构成财务、法律或其他专业建议,亦不应被解释为 MEXC 的推荐或认可。如需专家见解和深入分析,请造访 MEXC 学院。
4 最新动态
查看更多
特斯拉2026年第二季度财报日期:发布时间、网络直播及关键指标
特斯拉2026年第二季度财报定于2026年7月22日(星期三)美国股市收盘后发布,管理层计划于美国中部时间下午4:30 / 东部时间下午5:30主持实时Q&A网络直播。第二季度的更新和网络直播将通过特斯拉的投资者关系网站提供,并在电话会议后提供存档重播。
这不仅仅是另一个普通的特斯拉财报日。特斯拉已经报告了超预期的交付季度:在2026年第二季度,公司生产了451,758辆汽车,交付了480,126辆汽车,并部署了13.5 GWh的储能产品。
对于交易员来说,关键问题不再是特斯拉是否交付了更多汽车,这部分已经是已知事实。真正的问题是,这些交付是否足够盈利,储能业务的增长是否能支撑特斯拉更宏大的愿景,以及管理层能否证明其在人工智能、自动驾驶和Robotaxi(无人驾驶出租车)领域的投资正从“叙事”走向可衡量的业务进展。
2026/07/06
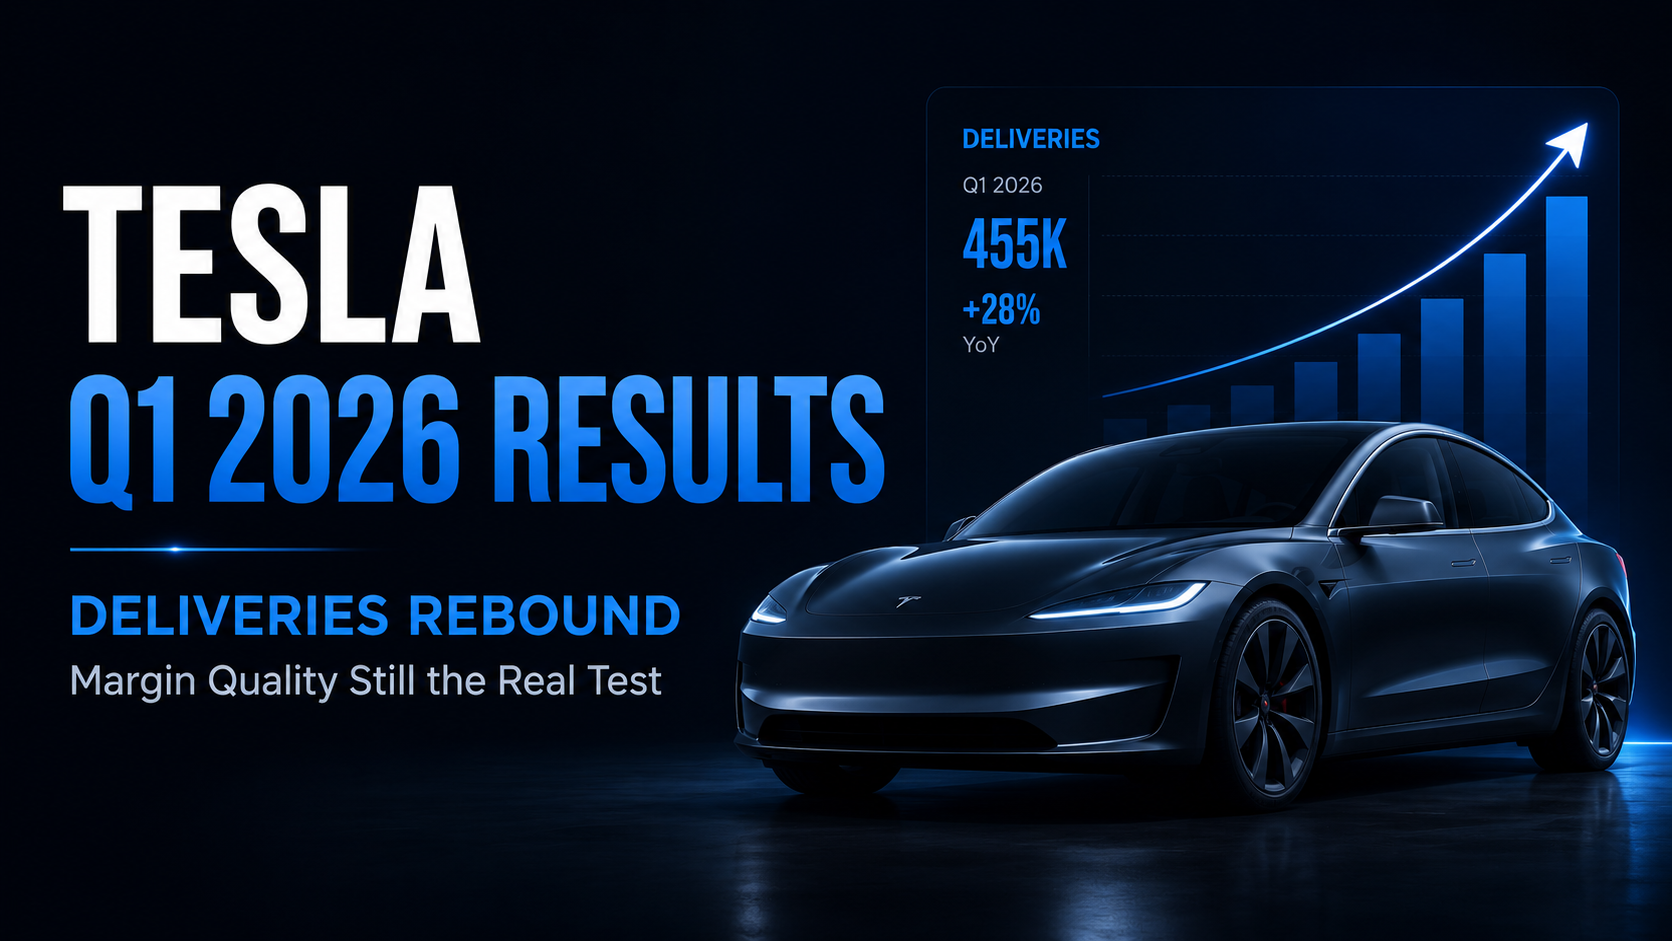
特斯拉2026年第一季度财报回顾:交付量反弹,但利润率质量仍是真正的考验
特斯拉于2026年4月22日美国股市收盘后公布了其2026年第一季度的财务业绩。该公司本季度交付了358,023辆汽车,创造了224亿美元的总营收,并报告归属于普通股股东的GAAP净利润为4.77亿美元。总GAAP毛利率提升至21.1%,而营业利润率达到4.2%。
核心信号不仅在于特斯拉的交付量从去年同期的疲软基数中恢复。更重要的问题是:更高的交付量、FSD相关营收、更低的单车成本以及改善的汽车毛利率,能否重建市场对特斯拉盈利能力的信心。对于寻找下一次TSLA财报日期或关注特斯拉财报的投资者来说,第一季度的表现为第二季度设立了一个关键考验:即销量的增长能否可持续地转化为更高质量的收益。
2026/07/09
苹果 2026 财年第二季度财报回顾:iPhone 营收与服务业务增长维持 EPS 预期
苹果于 2026 年 4 月 30 日发布了 2026 财年第二季度财报,涵盖截至 2026 年 3 月 28 日的季度。总营收达到 1112 亿美元,同比增长 17%,摊薄后每股收益(EPS)增长 22% 至 2.01 美元。苹果表示,该季度创下了公司 3 月份季度的总营收、iPhone 营收和 EPS 纪录,同时服务业务营收也创下历史新高。
这不仅仅是一份常规的硬件周期财报。苹果第二季度的业绩证明,iPhone 需求、服务业务增长以及积极的资本回报计划仍在共同支撑着该公司强大的 EPS 增长故事。对于寻找下一个苹果财报或 AAPL 财报更新的投资者而言,未来的关键问题是,在市场等待更强劲的 AI 和产品周期催化剂之际,苹果能否维持其溢价估值。
2026/07/09


您可能也会喜欢
热门
目前热门备受市场关注的加密货币
加密货币价格
按交易量计算交易量最大的加密货币